


Build Secure Scale
Your partner to build, secure and scale. One owner, from first design to daily operations.
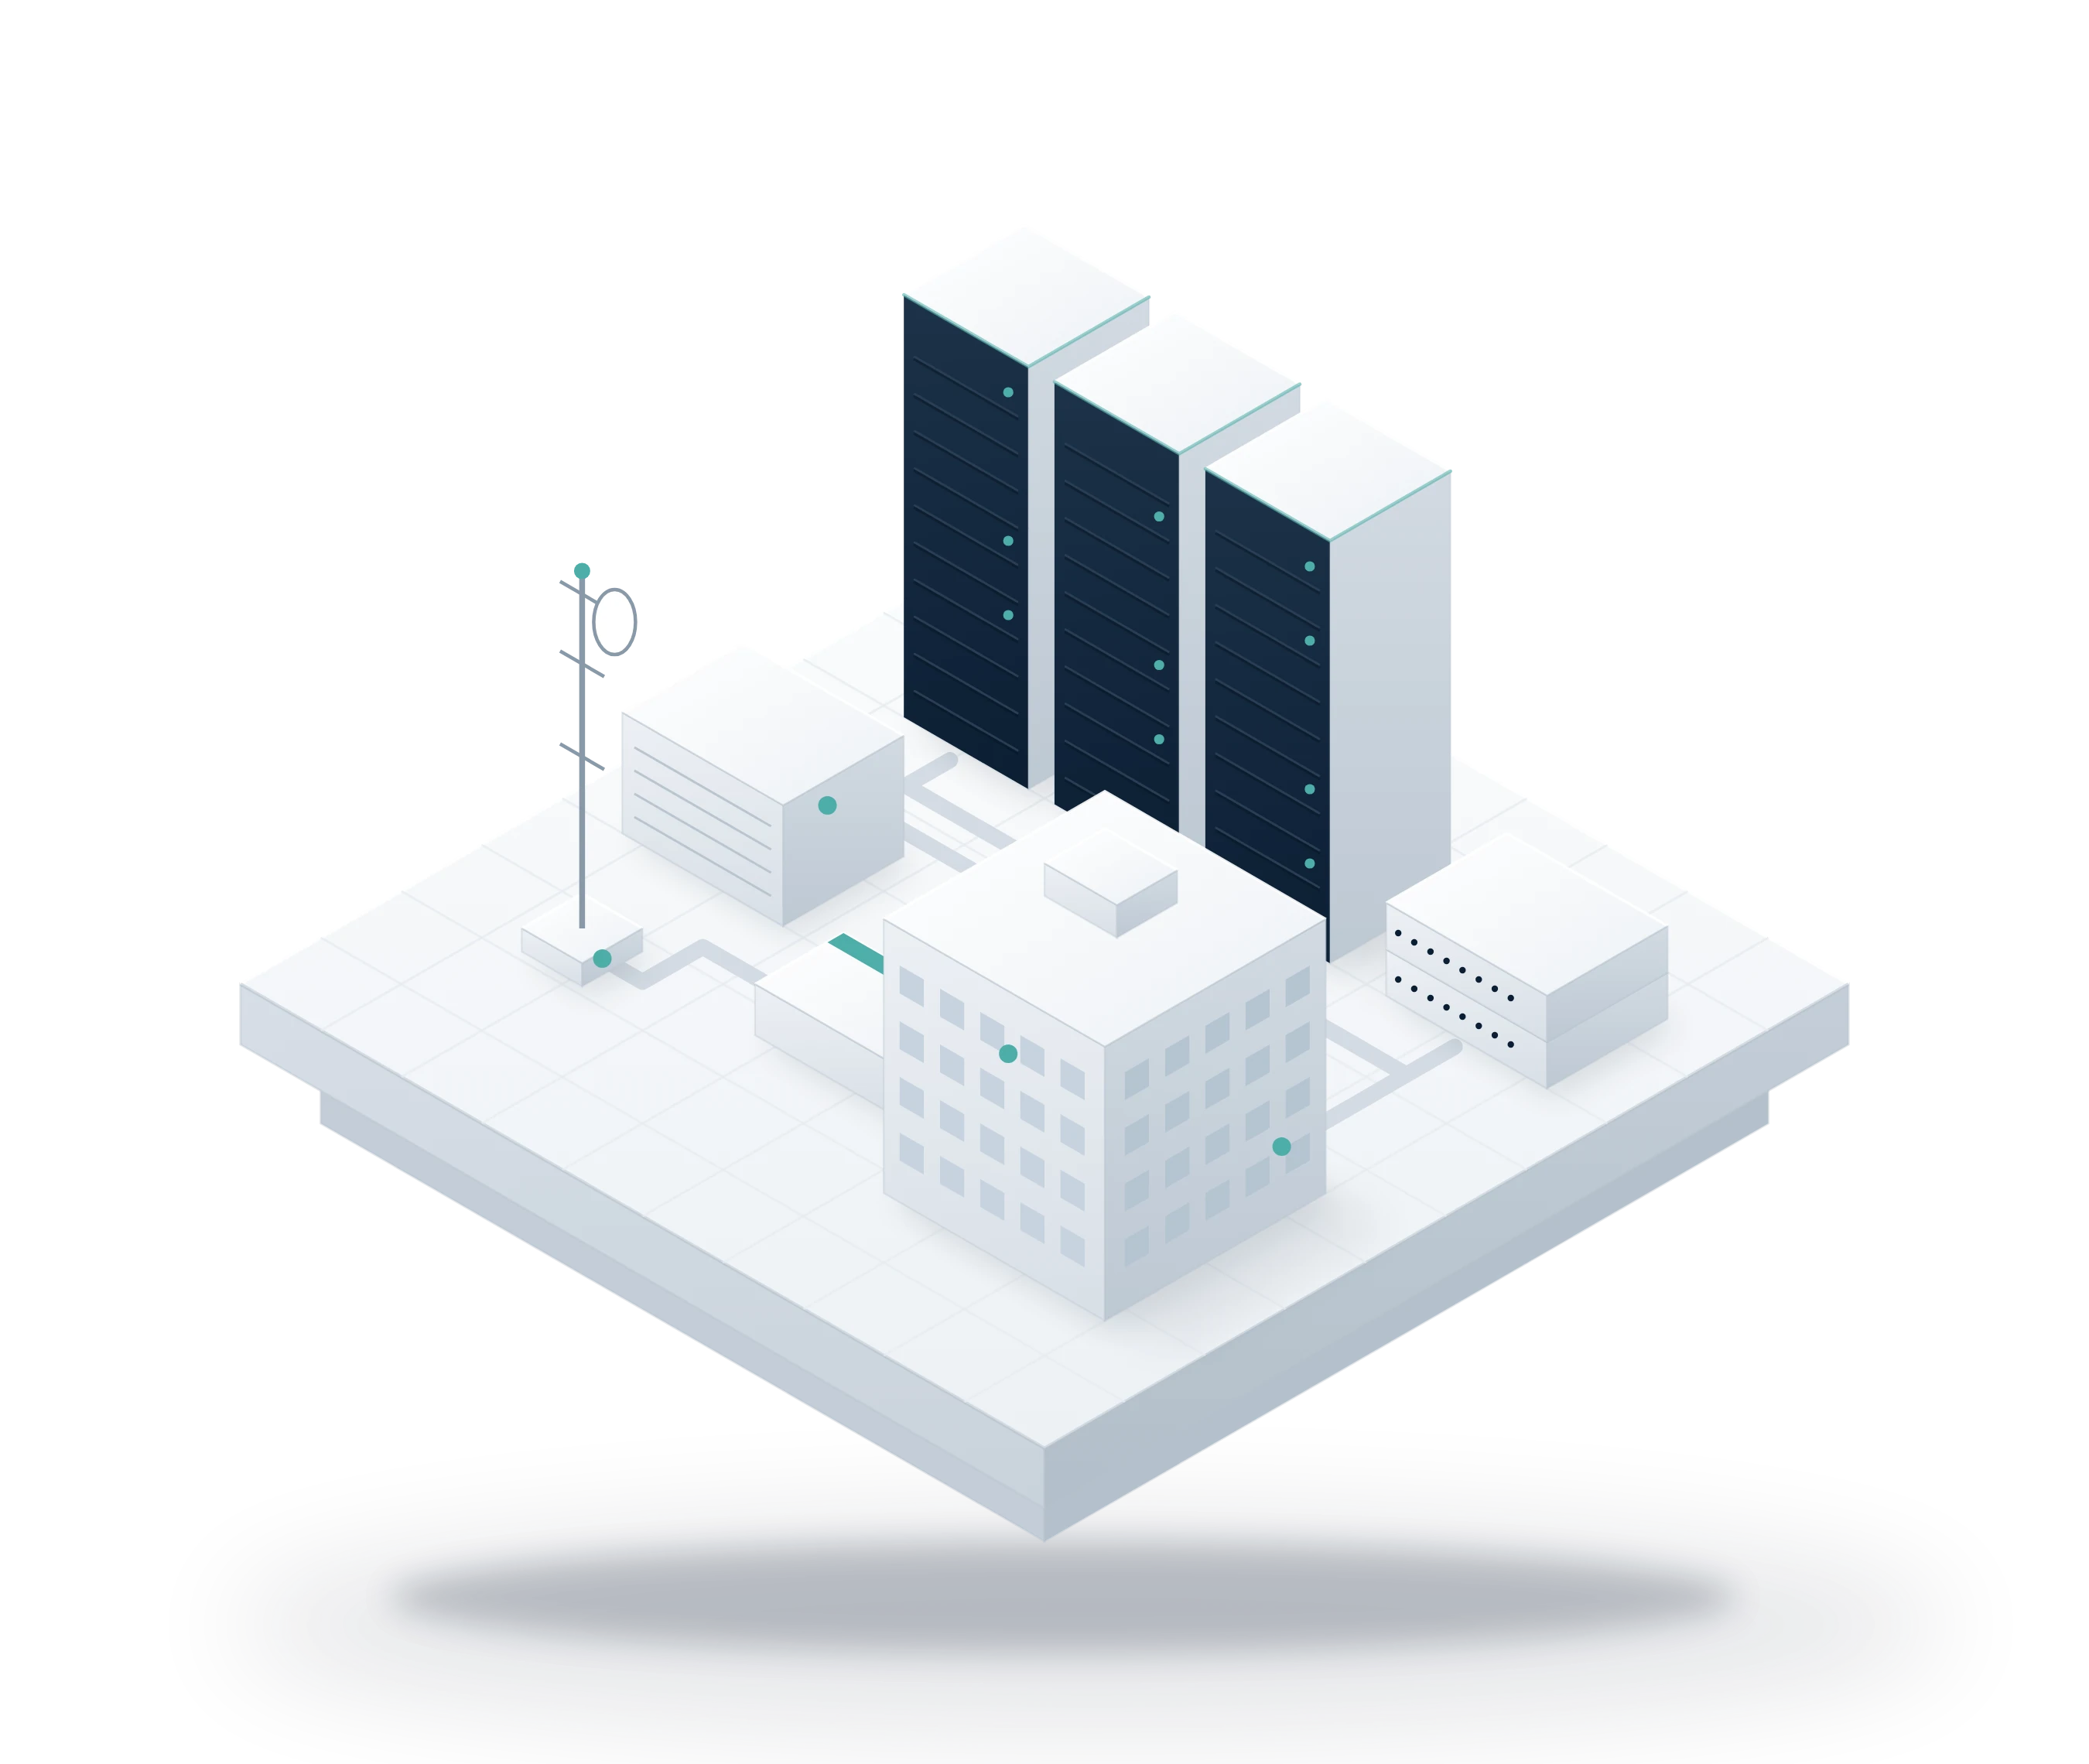
Illustration: a floating block of IT infrastructure with server racks, a core switch, a firewall, an office building and a radio mast. Data moves along the cable trays that join them.




What you can hold us to.
NetScale IT Services is a Bengaluru IT firm that designs, secures and runs enterprise IT across India.
Engineers, directly.
You connect directly with engineers who can diagnose the issue, design the solution and implement the fix. Nobody relays your problem through an account layer first.
How escalation worksFindings in writing, yours either way.
The assessment costs nothing. The written findings are yours whether we ever work together or not.
What the assessment includesFixed-scope phases. Stop at any boundary.
Each phase is fixed-scope and signed off separately. You can stop at any phase boundary, with everything built so far documented and handed over.
Terms you can read before you startDocumented and paired.
No client environment depends on a single NetScale engineer: every account is documented and paired. Runbooks, configurations and credentials are yours.
What is handed over
Scope first. Sign second.
Assessment before commitment, phased delivery, and operations afterwards, under one accountable partner.
You can stop at any phase boundary. The assessment is free, and each phase is priced in writing before it starts.How we engage
Work we can show you.
What clients brought us, what we found and what changed. Different industries, one way of working: scope first, findings in writing, one accountable owner.
- 01Retail · Datacentre, IndiaOne SLA for every datacentre server.15 minresponse, in the contract
- 02Software and IT consulting · BengaluruWorkplace as a service.3 monthsfull environment, scheduled from order
- 03Banking · Bengaluru technology centreDesk-ready device rollout.1 monthon site after the rollout
- 04Education technology · Laptops across departmentsWhat was really on the laptops, in one week.1 weekto find out what was on the laptops
Detailed case study on request. Client names and the full write-up of any engagement are shared in conversation.
All engagement storiesOur own systems
Certified to what we implement.
We run our own information security and privacy management systems under the same two standards we implement for clients.
- ISO/IEC 27001:2022Information Security Management System
- Certificate
- ISMS/4367/0926
- ISO/IEC 27701:2025Privacy Information Management System
- Certificate
- PIMS/54B0/0926
Your stack is our stack.
Our partners build the platforms; we make them work as one environment, with direct escalation into every vendor’s support organisation.
Questions buyers actually ask.
What does NetScale IT Services do?
NetScale IT Services is a Bengaluru-based IT infrastructure, cybersecurity and managed services company. It designs, secures and runs enterprise IT across India: networking and data centre, cybersecurity and compliance, cloud, AI and automation, and managed IT. Its ISO/IEC 27001:2022 and ISO/IEC 27701:2025 certificates cover “Cybersecurity services, Cloud services, AI and Automation Services, Managed services, Audit and Compliance Services and Training and Development services”. It is not Citrix NetScaler or Nscale.
What does the free assessment include, and what does it cost?
It costs nothing. One call with an engineer, then a written list of where your IT environment is exposed, by area: network and infrastructure, cloud and governance, identity and access, audit evidence. The written findings are yours whether we ever work together or not. If the report shows you do not need us, it says so.
Do we have to commit to a full project after the assessment?
No. Each phase is fixed-scope and signed off separately. You can stop at any phase boundary. Everything we build is documented and handed over as if you might leave tomorrow: runbooks, configurations and credentials are yours. Your own team can carry the work forward with or without us.
Who will we deal with day to day?
Engineers. You connect directly with the people who can diagnose the issue, design the solution and implement the fix. Nobody relays your problem through an account layer first. No client environment depends on a single NetScale engineer: every account is documented and paired.
How does NetScale help with the DPDP Act, and when does it apply?
Its substantive duties apply from 13 May 2027, under the DPDP Rules notified on 13 November 2025. We make the technical controls real: data mapping, access control, monitoring, one year of logs, breach intimation to the Data Protection Board and the people affected (without delay, then a detailed report to the Board within 72 hours) and vendor risk. Each comes with its evidence, aligned to ISO/IEC 27701. Legal interpretation stays with your counsel.
Do Indian companies have to report cyber incidents within 6 hours?
Yes. Under the CERT-In Directions of April 2022, organisations must report listed cyber incidents to CERT-In within 6 hours of noticing them. The Directions, in force since June 2022, also require ICT logs kept for 180 days within India and clocks synchronised to NIC or NPL time. Our SOC and logging work is designed around those three duties.
What is the difference between a SOC, MDR and a SIEM?
A SIEM (security information and event management) is the tool that collects and correlates logs. A SOC (security operations centre) is the team that watches it, continuously or in agreed windows. MDR (managed detection and response) is a SOC run as a service that also acts on its findings. We run managed SOC and MDR on estates we build or inherit.
Does NetScale work outside Bengaluru?
Yes. We are based in Bengaluru and serve enterprises and growing companies across India. We put engineers on site where the engagement needs them, and run the rest remotely. Multi-site programmes across several states are part of our existing work. Tell us where your sites are and we will say plainly how we would cover them.
Book a free assessment.
It costs nothing and commits you to nothing. Here is what happens after you send the form.
Scoping call15 minutes
An engineer calls to agree the type, the systems in scope and who needs to be in the room.
ReviewWith your team
We look at what you are running today against the control areas for the type you chose.
- Perimeter and segmentation
- Identity and privileged access
- Logging, retention and 6-hour reporting readiness
- Endpoint and email controls
- End-of-support inventory
- Single points of failure
- Backup and restore status
- Support and renewal map
- Cost against what was promised
- Region and residency
- Identity and access in the tenant
- Backup, disaster recovery and rollback
- Where personal data lives
- Security safeguards by control area
- Retention and deletion
- Breach response and evidence
Written findingsYours either way
A written list of where your IT environment is exposed. If the report shows you do not need us, it says so.
You decide whether to continue.
Prefer to talk? +91 96320 28993reachus@netscale.in